Research
Cryptography for real-world security problems.
The looming threat of a large-scale quantum computer necessitates
the move away from factoring and discrete-log based cryptosystems.
We have been working on several types of post-quantum systems,
including ones based on hard problems in
lattices,
isogenies, and based purely on
hash functions.
We have also been using lattices for
proofs of security
and
attacks.
Suppose a computationally weak device asks a powerful server to
perform a computation on its behalf. How can the weak device
trust the result? The beautiful field of succinct proof systems,
also called SNARKs, gives a practical solution. We build new
SNARK systems, such as
Bulletproofs,
Hyperplonk,
LatticeFold, and
Mangrove,
and are also exploring applications of these proof systems for
proving media provenance,
proving knowledge of a Lean proof,
distributed proving, and
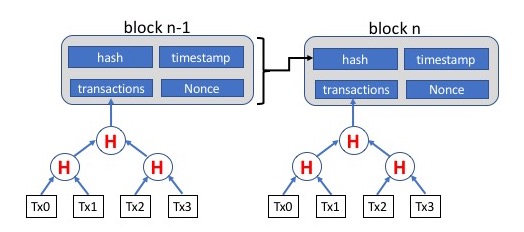
blockchains.
We are developing cryptographic tools with applications to
blockchains. We are also teaching a course on the topic,
CS251.
Export Control Warning
The US Government regulates the physical export or transmission of
cryptographic source and corresponding object code outside the borders
of the US and within the US when the recipient is an embassy or an
affiliate of a foreign government. Posting encrypted code to the
internet and making it publicly available is considered an export and
may entail US government notification requirements. Please see
Stanford's
Export Control Encryption Page
if you have a need to take, transfer or transmit Stanford-generated
encryption code outside of the US or to share it with US-based
representatives of foreign governments.